Your passwords are too weak!
Date: Feb. 7, 2024 Categories: passwords
Yes, it's a pain to change your passwords. But not nearly so painful as getting breached!
Getting hacked is miserable. When that happens you will then have to change all your passwords anyway. So make them stronger now.
UPDATE: See newer advice on passwords here: New 2026 Password Rule
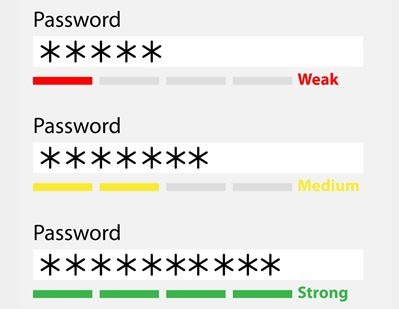
The new safety standard: At least 12 characters
Hacking software and readily available, powerful computers are game-changers. The old password rules are obsolete. Now your passwords need to be at least 12 characters long.
Online password generators
Good news! You can easily and safely create strong, 12-character or longer passwords.
Use an online password generator to create memorable, strong passwords. You can adjust the generators to produce passwords that work best for you.
In choosing an online password generator, you need to trust the organization behind it not to steal the passwords you generate! Nexcess is a large company with headquarters in Southfield, Michigan. I trust them, but still it is wise to take precautions.
Passwords-generator.org : https://passwords-generator.org/words from Reykjavik, Iceland.
Passwords-generator.org creates a password from two, three or more random words. You separate them by punctuation of your choosing or a 3-digit number or both. A two-word password created this way is very strong.
For example: partook773.incensed
What I don't like about Passwords-generator.org is that it comes up with very obscure words. That's good for strength be bad for memorization.
shoulder84.eye84
partook773.incensed
Testing your passwords is easy. For a typical password test, use this Bitwarden page:
https://bitwarden.com/password-strength/
For a really tough password test, use this Kaspersky page:
https://password.kaspersky.com/
The Kaspersky page expects you to use 12 characters unless you have a really hard-to-remember, complex 10- or 11-character password. When it fails a password, it always seems to report:
"Bad news - Frequently used words"
For example, Rxwp3drmp! passes the Bitwarden test with an estimate of 12 days to crack it with powerful computers. On the other hand, Kaspersky reports: "Your password is easily crackable. Frequently used words." Since when is "Rxmp" a word?
Kasperky gives much better ratings for passwords of 12 characters and up. You will be safer with passwords that pass the Kaspersky test.
Multiple-Word Passwords
A reasonable rule for your passwords is to use three random words of five or more letters including a capital letter, number and a period or hyphen.
The period or hyphen are not truly necessary for strength. Three words are satisfactory. But the capital, number and punctuation allow you to pass the password requirements often enforced by services you sign up for.
Caveat: Once quantum computing tools become widely available to hackers, passwords won't be safe. You will need passphrases.